
Sign up to save your podcasts
Or

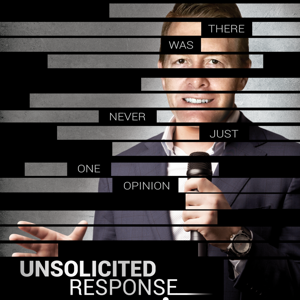


You know IT / OT integration is getting serious when the popular IT apps and services add OT extensions. The latest is ServiceNow's new OT Management Product.
James Destro of ServiceNow joins Dale Peterson on the Unsolicited Response show to talk about two main things.
1) How does OT Management get the OT asset inventory information? (and what is the single source of truth for OT asset inventory)
2) Once the OT asset inventory is in ServiceNow what types of workflows are envisioned that would be a big benefit to the asset owner.
Links:
Operational Technology Management 1-pager: https://www.servicenow.com/content/dam/servicenow-assets/public/en-us/doc-type/resource-center/solution-brief/uc-operational-technology-management-manufacturing.pdf
Detailed documentation of the Operational Technology Classes: https://docs.servicenow.com/bundle/quebec-servicenow-platform/page/product/configuration-management/concept/cmdb-ci-class-models-operation-technology.html
Asset Inventory Integrations: https://store.servicenow.com/sn_appstore_store.do#!/store/integrations?freeTrial=service_graph_certified&offeredby=servicenow%253Bpartners
Signup For Dale's Friday News & Notes at https://friday.dale-peterson.com/signup
ICS-Patch leverages the CERT/CC SSVC Decision Tree approach for determining what patches are important and a patching cadence. One of the most important customizations is all of the factors can either be pulled from an asset inventory or a CVSS feed. This means the evaluation of 10's or 100's of thousand asset/patch pairs can be automated and an ASAP, Scheduled, Defer answer provided.
Tweetme: @digitalbond
Subscribe to My Friday News & Notes: https://friday.dale-peterson.com/signup
This is Dale Peterson's weekly article originally published on 1 June 2021. Following the article Dale describes what we are looking for in S4 sessions and provides tips on what to do and not to do to increase your chances of getting on the S4x22 Stage.
S4x22 Call For Presentations: s4xevents.com/cfp
Subscribe to Dale's Friday News & Notes friday.dale-peterson.com/signup
Rob Lee of Dragos joins Dale Peterson on the Unsolicited Response show to discuss:
The Biden Administration efforts on OT Cybersecurity. What they are; the pro's and con's of these efforts; and where they might be successful.
Rob and Dale talk about their disagreement on where Detection products, and to a lesser extent threat intel, like Dragos and others offer should be considered in relation to other security controls and solutions.
The prospects for an entry level and mid level ICS Security Professional in 2021 and the upcoming years.
Subscribe to Dale's ICS Security Friday News and Note: https://friday.dale-peterson.com/signup
Dale's weekly article published on 25 May 2021 talks is triggered by a World Economic Forum report that on Resilience in the Oil and Gas sector.
Tweetme: @digitalbond
Sign Up For My Newsletter: https://friday.dale-peterson.com/signup
The episode begins with some announcements then
4:15 - Dale's Monologue/Rant on the Colonial Pipeline Incident. The increase it brings in attention, resources and expectations on a macro level. And the real action asset owners should be taking for this specific set of circumstances.
12:20 - Joel Langill joins the show and brings his experience on pipelines systems and their operations, plus a quick discussion on his new training.
30:45 - Rob Caldwell joins Joel and Dale. We talk about incident response in OT, and then answer questions from the LinkedIn and YouTube audience.
Links:
Six months since my Dec 2020 update ... the biggest change is major demand drivers; where is the Claroty and Nozomi funding round? and big cloud / enterprise products and services continue to introduce and up their offerings.
My weekly article published 18 May 2021.
Subscribe to my ICS Security: Friday News & Notes email: friday.dale-peterson.com/signup
Dale Peterson talks with Ulf Lindqvist and Laura Tinnel of SRI International about the recent LOGIIC report on the (in)security of safety instrumentations systems. Particularly the IMS/AMS components that configure and manage smart instruments.
They go over the three main findings, which are deadly serious and two have actionable mitigations.
They finish with a discussion of why there is not a hard recommendation to not allow the IMS/AMS to be on or accessible from the PCN.
Get the report at: https://www.logiic.org
See the S4x15 video on testing 114 DTM's at: https://youtu.be/qbno2woz7p4
Subscribe to Dale's ICS Security Friday News & Notes at: https://friday.dale-peterson.com/signup
The Colonial Pipeline incident highlights the need for an Enterprise Network Compromised Playbook. This and two other must haves are described in this article orginally published on 11 May 2021.
From the publisher's feed

373 Listeners

112,256 Listeners

8,078 Listeners

178 Listeners

20 Listeners
15,528 Listeners
18,920 Listeners