
Sign up to save your podcasts
Or



What challenges come up and how to overcome will be key here?
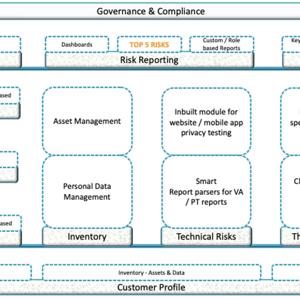
We will now look at Implementation and Rollout of the policies, processes we described. For SDLC, Engineering and Product technology controls; we will cover those as part of Privacy Engineering.
Our implementation comprises of the following key components
Governance and changes to the policies based on what we need to mitigate
Process and Procedure implementation
Technical areas implementation
The flow described in this season can be used by in either of the below situations:
For details, reach out to us on [email protected]; [email protected]; twitter: sameeranja, twitter: arrka2; Give a reference of this cast and avail credits on the platform usage and subscription. The Arrka Platform is made by SMB and for the SMB.
What to do when building tech. We need to enable privacy in software development as well. Here we will look at what needs to be done when building tech.
There are known models of Security in Design philosophy espoused by SSE-CMM (Systems Security Engineering – Capability Maturity Model) by SEI, ISO 27001:2013 (with controls in A.___ for Secure Coding), Common Criteria, NIST Guidelines among many others. OWASP has played a stellar role in ensuring Application Security is understood and applied to as well. These are terrific technology controls to have. The Software Engineering for Privacy is a Privacy by Design Philosophy and which is what we will map here with the Engineering process. The Engineering process here is Product Agnostic and Industry Agnostic.
The Privacy by Design therefore needs to be addressed at all aspects of the Organization and Product Development and Management. Consider Organization processes also as a product and unless we inculcate the "by design and default" philosophy in our organization; we will not be able to produce products, processes and by extension the comfort of privacy to our stakeholders.
The flow described in this season can be used by in either of the below situations:
For details, reach out to us on [email protected]; [email protected]; twitter: sameeranja, twitter: arrka2; Give a reference of this cast and avail credits on the platform usage and subscription. The Arrka Platform is made by SMB and for the SMB.
We have now reached a situation where we have implemented and have that euphoric feeling of "GREAT! I have done it! :)" Do enjoy the feeling and take a moment to celebrate this milestone.
For this is a milestone in the journey to keeping your organization protected. It is now nearly 23:59 and in a minute the clock will restart from 00:00. A new day dawns, and we must ensure the day goes on with our organization alert and ready. And so we come to - what do we keep doing.
What does the CISO do now?
What can go wrong?
The answer to both is “Plenty”. There are many things that can go wrong. The CISO is still not in monotonous mode, he/ she has plenty of new work to get into. However, the key to enabling maturity is to build in safeguards and control checkpoints so that issues can be identified early on and tackled. Many a times, we tend to get complacent here, and the processes and controls come to a comfort zone which makes us lazy and very very sloppy! This is something we need to guard against.
This episode tells you what you must keep doing. At some point (no later than a year), you will come back to Step 1. This is necessary because the world keeps changing and so we must adapt.
The flow described in this season can be used by in either of the below situations:
· you and work standalone/
· work with a consultant/expert
· can be used to run the show via the Arrka Privacy Management Platform (both for Security and Privacy).
For details, reach out to us on [email protected]; [email protected]; twitter: sameeranja, twitter: arrka2; Give a reference of this cast and avail credits on the platform usage and subscription. The Arrka Platform is made by SMB and for the SMB.
Awareness about Privacy has gone up around us, mainly thanks to the news about various breaches and fines. As a business owner/ shareholder/ stakeholder/ process owner; you should be worried since you can be the next big story. And this brings us to the core question – with so many laws and regulations coming around; what should we really be worried about? That we should be worried about Privacy and how as a business we manage – is a foregone conclusion. If you are wondering why you should be worried about Privacy; the whole uproar over every organisations policy change, various governments looking at pushing out law etc. Check out the various news.
Here, we are more looking at what Privacy is all about and as a company; how can we go about managing and ensuring compliance to the law around Privacy. This is a series of articles that we are bringing out to help aid the business in understanding the subject and also how they could approach the problem to solve.
The flow described in this season can be used by in either of the below situations:
For details, reach out to us on [email protected]; [email protected]; twitter: sameeranja, twitter: arrka2; Give a reference of this cast and avail credits on the platform usage and subscription. The Arrka Platform is made by SMB and for the SMB.
We now are aware of what Privacy means and implies to us as an organization.
In this episode, we will look at facets which allow you to determine if and to what extent Privacy is applicable to you. There are specific data which when processed by you requires you to embrace Privacy and there is also an ownership of data aspect that comes in.
The parameters which determine applicability of Privacy laws are:
The flow described in this season can be used by in either of the below situations:
For details, reach out to us on [email protected]; [email protected]; twitter: sameeranja, twitter: arrka2; Give a reference of this cast and avail credits on the platform usage and subscription. The Arrka Platform is made by SMB and for the SMB.
We have to identify the threats and risks so that we can enable appropriate controls and measures to mitigate.
Thank you for listening so far and appreciate any feedback coming our way. Now that we have identified data, applicability and I believe you are fairly sure that Privacy Compliance is applicable and mandatory to be applied. Therefore we now focus on what are the possible threats that will impact us.
There are various threat models and frameworks available. This article will not be an explanation of the various threat models and frameworks (I will list them in the end), however, we will focus on the basics and how we can arrive at threats and harms. Then you can choose any model to depict the threats and impacts.
The flow described in this season can be used by in either of the below situations:
For details, reach out to us on [email protected]; [email protected]; twitter: sameeranja, twitter: arrka2; Give a reference of this cast and avail credits on the platform usage and subscription. The Arrka Platform is made by SMB and for the SMB.
This is where policies starts to come in and we will explore the various sections needed.
Now that we have identified our risks, we need to work towards mitigating the risk. A good first step is to arrive at a statement of intent and then document it. This is an internal document prepared as a policy for the organization to follow. This is our Privacy Policy. A Privacy Policy should comprise of:
The flow described in this season can be used by in either of the below situations:
For details, reach out to us on [email protected]; [email protected]; twitter: sameeranja, twitter: arrka2; Give a reference of this cast and avail credits on the platform usage and subscription. The Arrka Platform is made by SMB and for the SMB.
Beyond the policy, there are other processes required like a Rights Management, Consent Management, Breach notification etc which we will dovetail into.
Now that the Privacy Policy is documented and approved; we move to roll out the Policy through the Organization. One such rollout is the Privacy Notice. However, there are a bunch of other processes that are required to be documented, rolled out and ofcourse – reviewed, audited, monitored! There are many frameworks available to help, globally NIST Privacy Framework https://www.nist.gov/privacy-framework/privacy-framework , ISO 27701, BS 10012 are good frameworks. In India, Data Security Council of India has come up with its own Data Privacy Framework https://www.dsci.in/content/dsci-privacy-framework-dpf%C2%A9 which is the DSCI DPF. The DSCI DPF is well rounded and can be used for implementation.
The Arrka Platform has its own framework, which we have made internally and used in the platform to provide a framework for organisations to implement.
The flow described in this season can be used by in either of the below situations:
For details, reach out to us on [email protected]; [email protected]; twitter: sameeranja, twitter: arrka2; Give a reference of this cast and avail credits on the platform usage and subscription. The Arrka Platform is made by SMB and for the SMB.
We have rolled out policies, procedures etc. However, it cannot be standalone and cannot be only a one-time review.
Review of implementations like Log Review, Incident Review, SIEM, Monitoring of the various access, set up a helpdesk etc. All of these can be implemented via Open Source solutions.
We have now defined policies, procedures, done the technical implementation using all the technologies we had within our setup. This is to ensure that we have generated optimum usage of everything we have spent on. Like learning, investment in technology is not wasted. We will always find use of this in every mode that is possible. Each desktop can be used, each laptop can be used in the defense of cybersecurity. It is not just the biggies like Firewall etc that come to the rescue. Many of the attacks happen through legitimate traffic (e-mail, while browsing) etc and hence the end point (as we call the desktop etc in security parlance) needs to have a defense mechanism as much as the others.
The flow described in this season can be used by in either of the below situations:
For details, reach out to us on [email protected]; [email protected]; twitter: sameeranja, twitter: arrka2; Give a reference of this cast and avail credits on the platform usage and subscription. The Arrka Platform is made by SMB and for the SMB.
We heard in the previous episode about implementing various tools and technology configurations. We now have a reasonable set of preventive techniques working. This however, does not mean that we cannot be hacked our data cannot be stolen. To identify strikes and probes happening against us, we need to set up an alerting mechanism as well. This is an additional layer in our defense and should be potent enough to identify any attacks coming towards us.
Let us examine some scenarios to define alerts we require
Someone is running a vulnerability scan on our networks from outside to identify loopholes in our system. This is called Reconnaissance in the security parlance. It is a series of queries lobbied over the network and targeted at all systems exposed to the public internet. For this, our internet firewall needs to be configured to watch and report. Firewalls have the alert identified however we need to be able to see this.
Internal users have copied data marked as confidential to a USB disk. Anti malware etc software running on end point computers have the ability to detect, we need a system to process this and report/ alert.
Someone is trying to login using a brute force attack. A brute force attack is about running a sequence of characters designed to guess a password. We need systems to report/ alert all such login failures. A typical event matching algorithm will watch for login failures happening within a minute and alert accordingly. This may also be happening to our Administrator type users, and now the threat increases.
The flow described in this season can be used by in either of the below situations:
· you and work standalone/
· work with a consultant/expert
· can be used to run the show via the Arrka Privacy Management Platform (both for Security and Privacy).
For details, reach out to us on [email protected]; [email protected]; twitter: sameeranja, twitter: arrka2; Give a reference of this cast and avail credits on the platform usage and subscription. The Arrka Platform is made by SMB and for the SMB.
From the publisher's feed