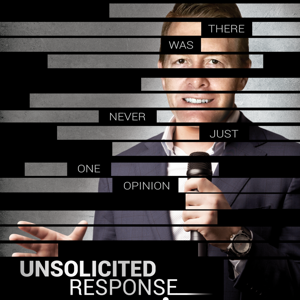
Unsolicited Response

Unsolicited Response

By Dale Peterson: ICS Security Catalyst and S4 Conference ChairNewsTechnologyTech News
Download on the App Store

Unsolicited Response episodes

  • State Of NERC CIP, European Update and OT Security Community

    Patrick Miller has OT cybersecurity experience as an asset owner, PacificCorp. As a regulator and one of the first NERC CIP auditors with WECC. As a community organizer creating and leading EnergySec and the BeerISAC. And as an entrepreneur creating and leading a number of consulting practices. He is currently the Founder of Ampyx Cyber.

    In this episode Patrick and Dale discuss:

    • Why Patrick changed the company name and selected Talinn as the location for the new European office.

    • The major differences in approaches to OT cybersecurity and risk management between Europe and the US. (more than just regulatory differences)

    • What has the EU learned or improved on regulation from NERC CIP.

    • What is the current state of NERC CIP regulatory risk? Are the regulated entities understanding and meeting the standards' requirements?

    • The challenge of slow NERC CIP modifications, eg virtualization and cloud.

    • Bad standard & good regulator v. good standard & bad regulator.

    • Should water follow the NERC CIP model as recommended by AWWA?

    • How Patrick is dealing with AI.

    Links

    • Ampyx Cyber: https://ampyxcyber.com

    • Patrick's Critical Assets Podcast: https://amperesec.com/podcast

    • Subscribe to Dale's ICS Security Friday News & Notes: https://friday.dale-peterson.com/signup

    • Advertise on Unsolicited Response: https://dale-peterson.com/advertising/

    47 min
  • Q1: ICS Security In Review

    Emma Stewart joins Dale to discuss the 3 big OT & ICS security stories from the first quarter. They end by giving their win, fail and prediction for Q1.

    50 min
  • Predictions Analyzed

    In this solosode episode Dale reviews the status of his three predictions from the Q1, 2 and 3 quarter in review episodes and answers a listener question.

    12 min
  • CISA Attack Surface Scanning Service

    Dale is joined by Steve Pozza, CISA Section Chief of Operational Resilience, and Tom Millar, CISA Branch Chief of Resilience, to discuss some of CISA's security services for asset owners. They discuss:

    • The Internet accessible attack surface enumeration and vulnerability scanning surface.
    • Asset owners can buy products or services to do this. Why is the government doing this?
    • What CISA is doing with this attack surface data?
    • How is CISA measuring the success of this service offering?
    • Other broadly available services and tools, the cybersecurity performance goals (CPG assessment) ~500 done in 2023 (and their thinking about self-assessments), Malcom traffic analysis tool, and a couple of other tools.

    Links

    • CISA Vulnerability Scanning Services
    • Malcolm Tool
    31 min
  • Engineering-Grade OT Security with Andrew Ginter

    Andrew Ginter published his third book this year: Engineering-Grade OT Security. Dale interviews Andrew on the book including:

    • Who was the target reader that Andrew wrote the book for?
    • Do (should) professional engineers lose their licenses for poor and dangerous cybersecurity design and deployments?
    • The use of the term engineering grade, and how he defines it.
    • Unhackable protection and safety controls as a major part of engineering grade.
    • Unidirectional (one-way) network devices as the only security control listed as engineering grade. Is one-way from the enterprise network to the OT network engineering grade?
    • Given the ICSSTRIVE/Waterfall report that 75% of all cyber incidents affecting operations are due to ransomware on IT, should asset owners prioritize address this issue or engineering grade security first?
    • What is keeping Andrew working rather than retiring

    Links

    • Complete this form to get a free copy of the book
    54 min
  • Asset Inventory, Lawyers, and AI

    This week is a Dale Peterson solosode.

    Updates and Announcements

    Dale provides updates about S4x24 ticket sales and announces the Women In ICS Security program and sponsor package.

    Main Topics

    1. Asset Inventory in Cybersecurity: Dale challenges the common security mantra "You can't protect what you don't know," using examples from both physical and cyber domains. He notes many of the comments on this week's article missed the main point, and he gives hints on the next two asset inventory articles.
    2. Legal and Regulatory Issues in Cybersecurity: Dale emphasizes the importance of domain expertise whether it be cybersecurity or the legal profession. He previews upcoming keynote interviews with legal experts and advises cybersecurity professionals against making legal analyses without proper expertise.
    3. Artificial Intelligence in Cybersecurity: Dale reveals that most AI submissions for S4 were broad and hand wavy. This isn't wrong, but most have heard this info by now. He then discusses the need for focusing on specific, real-world applications of AI and stresses the importance of measurable improvements in this age of experimentation.
    28 min

About Unsolicited Response

From the publisher's feed

Dale Peterson interviews the innovators in ICS / SCADA cyber security as well as the top talent in related fields. It is the podcast for those who want more information similar to what is presented at…

More shows like Unsolicited Response

Risky Business by Risky Business Media

Risky Business

373 Listeners

The Daily by The New York Times

The Daily

112,256 Listeners

Darknet Diaries by Jack Rhysider

Darknet Diaries

8,078 Listeners

Cybersecurity Today by David Shipley

Cybersecurity Today

178 Listeners

The Industrial Security Podcast by PI Media

The Industrial Security Podcast

20 Listeners

The Rest Is History by Goalhanger

The Rest Is History

15,528 Listeners

The Mel Robbins Podcast by Mel Robbins

The Mel Robbins Podcast

18,920 Listeners